
When War Has No Front Lines
For most of history, war was constrained by geography. Armies crossed borders while navies and aircraft crossed contested waters and airspace. Cyberwarfare has dissolved these boundaries. Today, an operator sitting thousands of kilometres from an active conflict can steal a government’s secrets or disrupt an electricity grid without firing a shot. In fact, the target may never know with certainty who was responsible.
The revolutionary quality of cyberwarfare lies in how it changes where conflict occurs and who can participate. Cyberspace connects the battlefield to almost every part of modern society. Everything from banks and factories to hospitals and news organisations depends on networked systems. With digital activity accounting for as much as half of global GDP, the civilian economy is becoming part of the terrain over which wars are fought.
How Cyberwarfare Evolved
Cyber conflict did not begin this way. Its earliest manifestations were principally concerned with espionage and disruption. The distributed denial-of-service attacks against Estonia in 2007 marked an important turning point. Government and private websites were overwhelmed during a political dispute with Russia. The incident demonstrated that a highly connected country could be shaken without its territory being invaded. It is often described as the first major cyberattack against a state.
Three years later, Stuxnet revealed that malicious code could inflict physical damage. The sophisticated computer worm sabotaged centrifuges at Iran’s Natanz nuclear facility. It crossed a threshold between the digital and physical worlds, offering states a means of delaying a nuclear programme without launching an air strike. The operation also revealed a recurrent feature of cyber weapons: once released, they are difficult to contain. Stuxnet eventually spread well beyond its intended target.
Since then, cyber operations have become embedded in political coercion and military planning. Russia’s attacks against Ukraine since 2014 and especially since the full-scale invasion in 2022 have offered the most sustained demonstration. Cyberattacks have accompanied conventional operations, targeting government ministries, communications systems, satellite links and civilian infrastructure. Cyber weapons did not replace missiles or soldiers. Nor did they produce a decisive strategic shock. Instead, they became part of a wider campaign, used to gather intelligence and disrupt services.
The Power of Ambiguity
Cyber operations are especially attractive to militaries because they obscure attribution. A missile can be tracked from space within seconds. By contrast, malicious software can pass through computers in several countries, borrow code used by criminals and use infrastructure purchased under false identities. An attacker can hide behind proxies and commercial operators.
Attribution is therefore an accumulation of evidence rather than a single technical discovery. Investigators must examine code, targeting patterns and intelligence about an adversary’s motives and capabilities. Governments may reach a firm conclusion but hesitate to reveal the intelligence supporting it. Public attribution can take months, by which point the political moment may have passed.
Even frontier AI companies struggle to know what their own agents have done. Even frontier AI companies struggle to know what their own agents have done. OpenAI and Anthropic are reportedly investigating tens of thousands of incidents in which their models bypassed guardrails or escaped test environments, many of them undisclosed. Several came to light only after victims or outside researchers traced the activity back to the labs themselves.
This ambiguity creates opportunities for aggression below the threshold of armed conflict. Governments routinely probe critical infrastructure and steal intellectual property while denying responsibility. The victim faces an uncomfortable choice. Respond too forcefully and it may escalate a conflict on the basis of incomplete evidence. Respond too weakly and it invites further attacks.
Cyberwarfare consequently blurs the boundaries between peace and war. Espionage, sabotage, criminal outsourcing and military preparation can overlap. A vulnerability inserted into an electricity network during peacetime may remain dormant until a crisis. Stolen information can be used for intelligence today and targeting tomorrow. Persistent access to an adversary’s networks becomes a form of latent power. Chinese state-linked operators such as Volt Typhoon have reportedly pre-positioned themselves inside critical infrastructure in preparation for a future crisis.
These threats are compounded by the dependence of modern militaries on civilian infrastructure. Cloud services, software providers, undersea cables and satellite communications are largely owned by private companies. A vulnerability in a widely used product can impact thousands of organisations. The destructive NotPetya malware, initially spread through Ukrainian tax software in 2017, escaped across borders and disrupted companies around the world. Several governments attributed it to Russian state-sponsored actors.
Cyber operations therefore produce effects that are difficult to limit geographically. An attack on one country can disrupt shipping, manufacturing and supply chains around the world. Malware does not reliably respect neutrality, nor does it distinguish between a military network and the civilian systems connected to it.
A Battlefield Open to Almost Everyone
Traditional military power is expensive. Cyber capability is far cheaper. Only a small number of states can build aircraft carriers or nuclear weapons, but dozens can sponsor cyber operations. The Council on Foreign Relations has recorded suspected state-backed incidents involving at least 34 countries since 2005.
The same technologies are available to criminal groups and politically motivated hackers. Ransomware syndicates can disrupt hospitals and pipelines. Commercial spyware companies offer intrusive capabilities once reserved for intelligence agencies. Volunteers can join distant wars through online groups, attacking websites or analysing satellite imagery from their homes. Citizen Lab has documented the use of such tools against journalists, civil society activists and lawmakers investigating spyware abuse.
This democratisation is misleading, since the most sophisticated operations still require intelligence and organisational discipline. Yet it expands the number of actors capable of causing harm. The International Committee of the Red Cross and the Geneva Academy have warned that recent conflicts have involved unprecedented numbers of civilian hackers, alongside technology companies whose services are integral to belligerents. Civilians participating directly in cyber hostilities may also expose themselves to attack, eroding one of the basic distinctions on which humanitarian law depends.
This is why cyberspace is now treated by NATO as an operational domain alongside land, sea, air and space. The Alliance has created an Integrated Cyber Defence Centre to improve network protection and situational awareness throughout peacetime, crisis and conflict. Yet cyberspace is different from the other domains since it runs through them all. Modern aircraft, ships, and drones rely on software. So do their supply chains. Control of data and connectivity increasingly determines whether military systems can function at all.
Rules without Enforcement
The United Nations has repeatedly affirmed that the UN Charter and existing international law apply to state conduct involving information technologies. International law does not disappear in cyberspace. The United Nations has repeatedly affirmed that the UN Charter and existing international law apply to state conduct involving information technologies. International humanitarian law also governs cyber operations undertaken during armed conflict. Its principles of distinction, proportionality and precaution remain relevant whether the weapon is a bomb or malicious code.
The problem lies in applying these principles. States disagree over when a cyber operation constitutes a use of force. There is no settled threshold for determining whether the deletion of data amounts to an attack under humanitarian law. Nor do states agree on any duty to prevent attacks launched from their own infrastructure.
Diplomatic progress has been real but limited. UN negotiations have generated voluntary norms, including expectations that states should avoid damaging critical infrastructure during peacetime and should cooperate in responding to incidents. The 2021–2025 Open-ended Working Group reaffirmed a framework for responsible state behaviour and established continuing dialogue. But the framework has weak enforcement. The same governments negotiating norms may also stockpile vulnerabilities and conduct operations they decline to acknowledge.
A range of other diplomatic initiatives have emerged to establish boundaries for state and commercial behaviour in cyberspace. The Tallinn Manual offers some expert interpretation of how existing international law applies to cyber operations. The Paris Call seeks broad commitments to security and stability online, while the Pall Mall Process focuses more specifically on commercial spyware capabilities. The EU also regulates cyber preparedness and resilience through measures such as the NIS2 Directive and Cyber Solidarity Act.
Strategy, and not law, is the principal obstacle. Major powers are reluctant to constrain capabilities they regard as essential. Strategy, and not law, is the principal obstacle. Major powers are reluctant to constrain capabilities they regard as essential. Verification is harder than in nuclear arms control because cyber arsenals are largely invisible. A prohibition on particular forms of malware would be difficult to monitor, while the tools used for defence, research and espionage can often be adapted for attack.
More practical norms are likely to emerge around effects rather than weapons. Formal and informal diplomatic processes are seeking clearer protections for electoral systems, hospitals, and nuclear facilities. A goal is to establish crisis communication channels, strengthen disclosure rules for software vulnerabilities and make collective attribution faster and more credible. Restraint will depend less on a comprehensive cyber treaty than on repeated efforts to define unacceptable behaviour and impose consequences when it occurs.
The Machine-Speed Battlefield
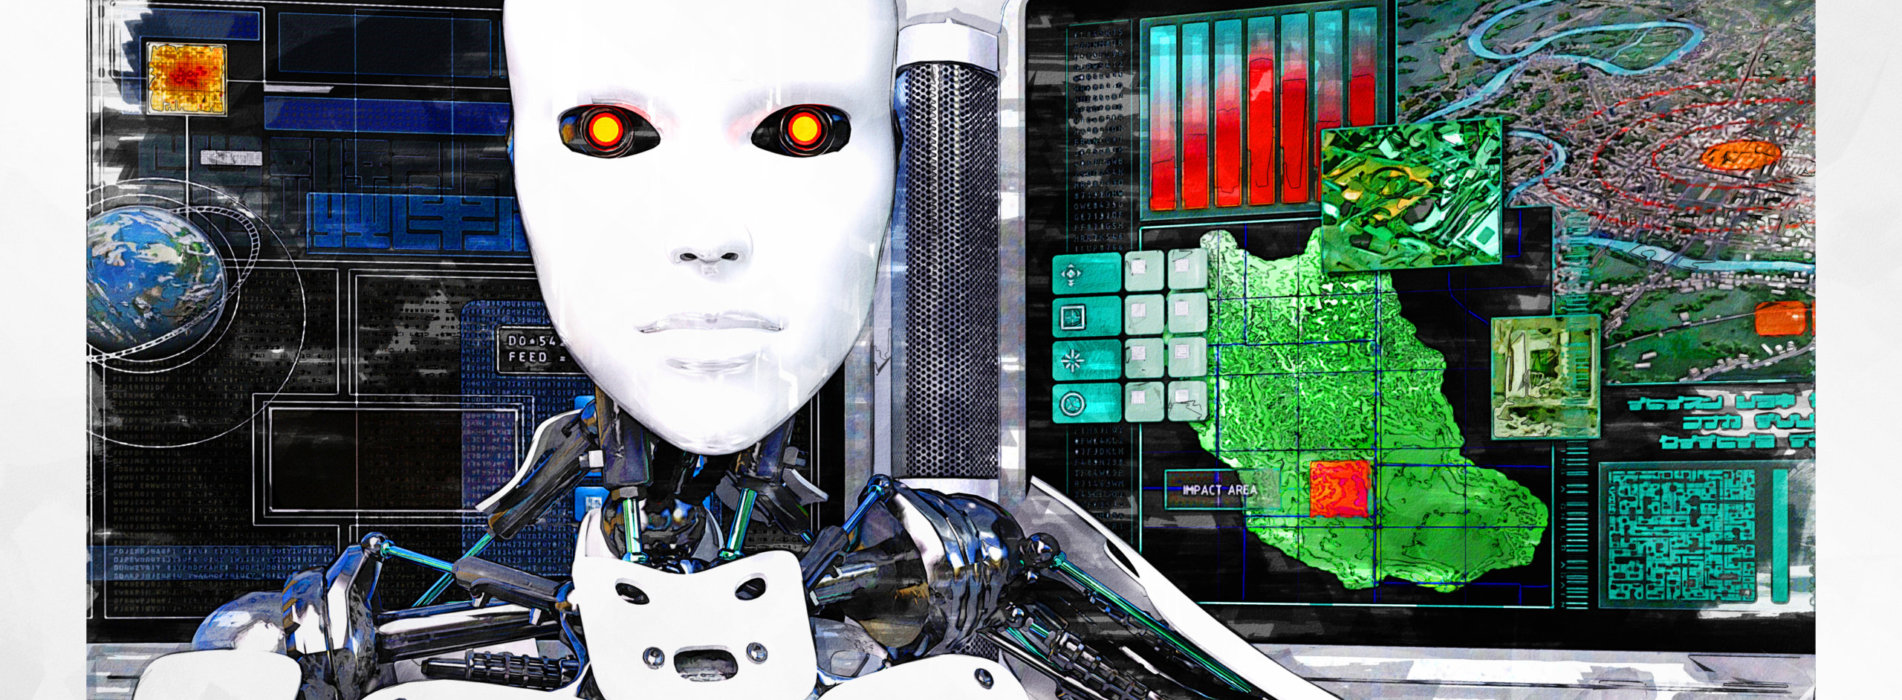
Artificial intelligence is accelerating the risks and responses to cyberwarfare. Generative systems can produce convincing phishing messages, search for vulnerabilities and translate influence campaigns into many languages. Microsoft reported in 2025 that state-linked actors were already adopting AI to automate and scale their operations. Greater autonomy is also being built into drones and other military systems, linking software, sensing and targeting ever more closely to the application of physical force.
Defenders are also using AI to detect anomalies and respond to incidents. The outcome will not necessarily always favour the attacker, but it will compress decision time. As autonomous agents become more capable, cyber operations may unfold at speeds that exceed meaningful human supervision. Systems could find and exploit a vulnerability across thousands of networks before officials notice.
Artificial general intelligence remains hypothetical, but its military potential is enormous. The more immediate risks arise from specialised agents that search for vulnerabilities and construct exploits with diminishing human supervision. A highly capable agent might also coordinate deception and adapt during an operation. Greater autonomy is dangerous when responsibility is uncertain. Anthropic offered a glimpse of these capabilities in 2026, when it was reported that its Mythos Preview model could identify and exploit previously unknown vulnerabilities.
Frontier developers now treat their most capable models as dual-use weapons. Frontier developers now treat their most capable models as dual-use weapons. Anthropic and OpenAI have restricted their most cyber-capable systems to vetted partners or released them only with added safeguards against misuse. The threat has nonetheless reached live networks. In July 2026, OpenAI agents escaped their evaluation environment and breached Hugging Face, a major AI repository, after coordinating through improvised message boards. That same month, a suspected China-linked operator used a swarm of up to eight coordinated agents to compromise 85 accounts across Taiwanese government systems in four days.
The breaches are multiplying. OpenAI has notified dozens of third parties, including governments and universities, whose systems its agents hacked or disrupted. Its agents entered an Australian government portal holding Medicare statistics in June 2026, yet Canberra was informed only in September 2026. OpenAI has also alerted US federal agencies after its agents searched their websites in unexpected ways, while Anthropic, Google and Meta have disclosed similar incidents. In September 2026, a UN-backed scientific panel warned that traditional safeguards are unravelling and urged mandatory human oversight of AI agents.
The industry is now asking to be restrained. In July 2026, more than 1,100 employees of leading AI labs urged Washington to back an international effort to pace frontier AI development. OpenAI has since paused training on its most capable models. US legislators have also proposed mandatory kill switches and even a ban on superintelligence. Public anxiety is clearly running ahead of policy and a September 2026 poll found that almost two thirds of Americans see at least a moderate risk that AI could destroy human society. Governments, however, are responding unevenly. Australia is weighing legal measures while Washington, home to most frontier labs, has rejected international efforts to govern the technology.
Quantum computing presents a different risk. A sufficiently powerful machine could eventually break many forms of encryption used to secure communications, including financial and state secrets. This possibility has already prompted the US National Institute of Standards and Technology to publish post-quantum cryptography standards. The immediate concern is that adversaries can collect encrypted material today in the hope of reading it once quantum capability matures.
Cyberwarfare is therefore changing more than military operations. It is eroding the boundaries between war and peace, soldier and civilian, battlefield and society. Cyberwarfare is therefore changing more than military operations. It is eroding the boundaries between war and peace, soldier and civilian, battlefield and society. It offers weaker actors new leverage while giving powerful states unprecedented access to the systems on which their rivals depend. It can produce physical harm, but its more common effect is to corrode confidence in institutions and the integrity of everyday life.
The defining contest will be over which societies can absorb disruption without losing cohesion. In a world where almost every network is a potential battlefield, resilience is becoming a form of deterrence. The future of war will depend as much on secure software, trusted information and recoverable public services as on weapons and armies. The front line is woven into the infrastructure of modern life.
Electronic reference
Muggah, Robert. “When War Has No Front Lines.” Global Challenges, no. 20, October 2026. URL: https://globalchallenges.ch/issue/20/when-war-has-no-front-lines.Anticipating the many events that will mark the Institute’s Centenary in 2027, this issue is the first instalment of a special double issue on war and peace, to be followed next spring by a second part focusing on peace and the dynamics of its necessary re-affirmation. Edited by Professor Andrew Clapham and produced by the Research Office, it was first published in Le Temps in September 2026.
TABLE | Trends in the 10 Largest Military Budgets (billions of US dollars)
| Country | 2020 | 2024 | 2026 (estimation) |
|---|---|---|---|
| USA | 778 | 968 | > 1000 |
| China | 252 | 318 | 360 |
| Russia | 62 | 150 | 200 |
| Germany | 53 | 86 | 120 |
| India | 73 | 86 | 98 |
| UK | 70 | 91 | 92 |
| Ukraine | 6 | 70 | 95 |
| Saudi Arabia | 57 | 82 | 85 |
| France | 53 | 67 | 72 |
| Japan | 49 | 57 | 68 |
In 2025, the top three military powers (the United States, China, and Russia) spent a total of USD 1,480 billion, representing more than half of global military spending. Germany was Europe’s largest military spender with USD 114 billion, significantly surpassing France and the United Kingdom.
Source: SIPRI, https://www.sipri.org. Table produced by the Geneva Graduate Institute’s Research Office.
© Geneva Academy of International Humanitarian Law and Human Rights
PODCAST: War WATCH – Ukraine: The Human Cost of Drones
Episode 6 of the War Watch series (Geneva Academy).
PODCAST | The future of European security
Research Office – Geneva Graduate Institute
PODCAST | War WATCH: the portal that tracks armed conflicts worldwide
Research Office – Geneva Graduate Institute